Central Bank of Egypt Launches Second Edition of National Cybersecurity Framework at Cairo ICT 2026
The Central Bank of Egypt (CBE) has announced the launch of the second edition of its integrated regulatory cybersecurity framework for the banking and financial sector during the 30th edition of Cairo ICT 2026. The new edition aims to strengthen the protection of financial institutions, enhance their readiness to address cyber threats, and keep pace with risks associated with emerging technologies and artificial intelligence.
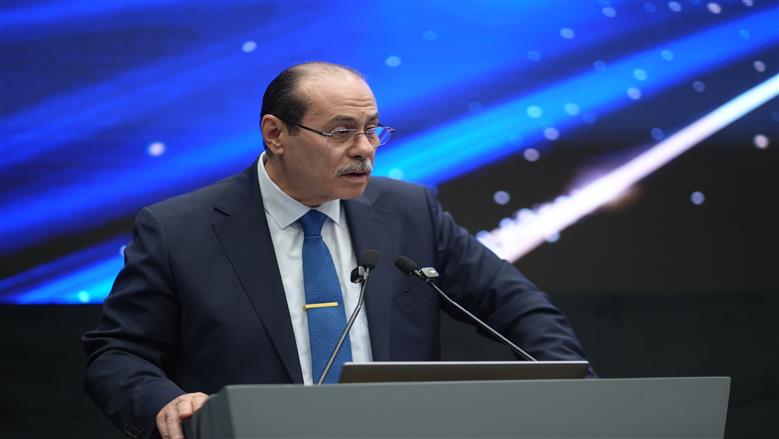
Tarek El-Khouly, Deputy Governor of the Central Bank of Egypt, delivered remarks on behalf of CBE Governor Hassan Abdalla, explaining that the new edition represents a significant shift in cybersecurity supervision and protection. It moves away from traditional assessment methods towards a dynamic, risk-based model that considers each institution’s actual risk exposure and links security controls to its business size, nature of operations and level of threats.
Risk Assessment and Cyberattack Simulation Exercises
El-Khouly noted that cybersecurity challenges increasingly affect financial institutions’ ability to maintain service continuity. This makes it essential to establish an integrated framework for risk management, rapid incident response and the exchange of alerts across the financial sector.
He explained that the Central Bank is working to provide specialized training for banks’ information security teams, including practical cyberattack simulation exercises. These involve teams carrying out simulated attacks and others responsible for defending against them, allowing institutions to assess the effectiveness of their protection systems, identify weaknesses, address security gaps and exchange expertise. He also noted that the CBE aims to make these exercises available free of charge.
The implementation of the new framework will be accompanied by a grace period, to be determined in coordination with banks, allowing them to align their operations with the requirements. On-site supervisory teams will also assess institutional readiness and identify security gaps.
El-Khouly stressed the importance of investing in attracting and retaining specialized information security professionals.
He also revealed that three applications have been submitted to obtain licences for establishing digital banks. He emphasized that the expansion of banking services through digital channels makes technological infrastructure and cybersecurity readiness essential requirements for ensuring the continuity of these banks’ operations.
38 Banking Institutions Assessed Under the First Edition
Sherif Hazem, Head of the Cybersecurity Sector at the Central Bank of Egypt, said that the second edition builds on ongoing efforts to establish a unified national reference for assessing financial institutions’ capabilities in responding to cyberattacks and protecting assets, data and customers’ savings.
He explained that the first edition, launched in 2022, helped standardize the assessment framework across the banking sector. A total of 38 banking institutions were assessed over eight months, based on three main pillars: people, technology and processes.
This was followed by a ten-month period dedicated to reviewing corrective action plans, identifying security gaps and determining the requirements needed to address them.
Hazem added that the second edition was developed in cooperation with PwC and draws on more than 38 international standards. It is designed to reflect the latest global practices and address emerging risks associated with artificial intelligence, cloud computing, the Internet of Things and quantum computing.
Zero Trust and Quantum-Resistant Encryption
Hazem explained that the new framework adopts a risk-based assessment approach tailored to each institution’s nature and operational scale.
It also incorporates the concept of Zero Trust, which requires continuous verification before granting access to systems and digital resources.
In addition, the framework addresses potential risks associated with quantum computing by encouraging preparations for the adoption of quantum-resistant encryption technologies.
It also introduces “risk drivers” to clarify the potential consequences of failing to implement security controls, alongside practical guidance to help institutions understand and apply the requirements.
The second edition further includes an enhanced model that links the maturity of cybersecurity capabilities to institutions’ actual effectiveness in managing cyber risks.
Hazem highlighted the importance of developing specialized professionals in cooperation with relevant entities and the Egyptian Banking Institute, while addressing skills gaps through dedicated programmes and practical training.
He stressed that building national cybersecurity capabilities helps strengthen customer confidence, protect savings and support the financial sector’s ability to attract investment.
Cairo ICT 2026 Highlights Artificial Intelligence and Digital Payments
The 30th edition of Cairo ICT 2026 is being held from November 7 to 10 at the Egypt International Exhibition Center in New Cairo, under the theme “AI in Action.”
The exhibition coincides with the 13th edition of the Digital Payments and Financial Inclusion Exhibition and Conference, PAFIX, held under the auspices of the Central Bank of Egypt.